Why Security-First Website Platforms Matter for Online Businesses
A website is no longer just a digital brochure.
For many businesses, it is the place where customers discover products, submit inquiries, create accounts, make payments, place orders, and share personal information.
That makes website security a business requirement—not simply a technical concern.
Yet security is often treated as something businesses add after building their website.
Install a security plugin.
Add a firewall.
Configure a security service.
Install another plugin.
Monitor suspicious activity.
Update everything regularly.
This approach can work, but it can also create unnecessary complexity.
A modern approach is to start with a different question:
What if security was part of the platform from the beginning?
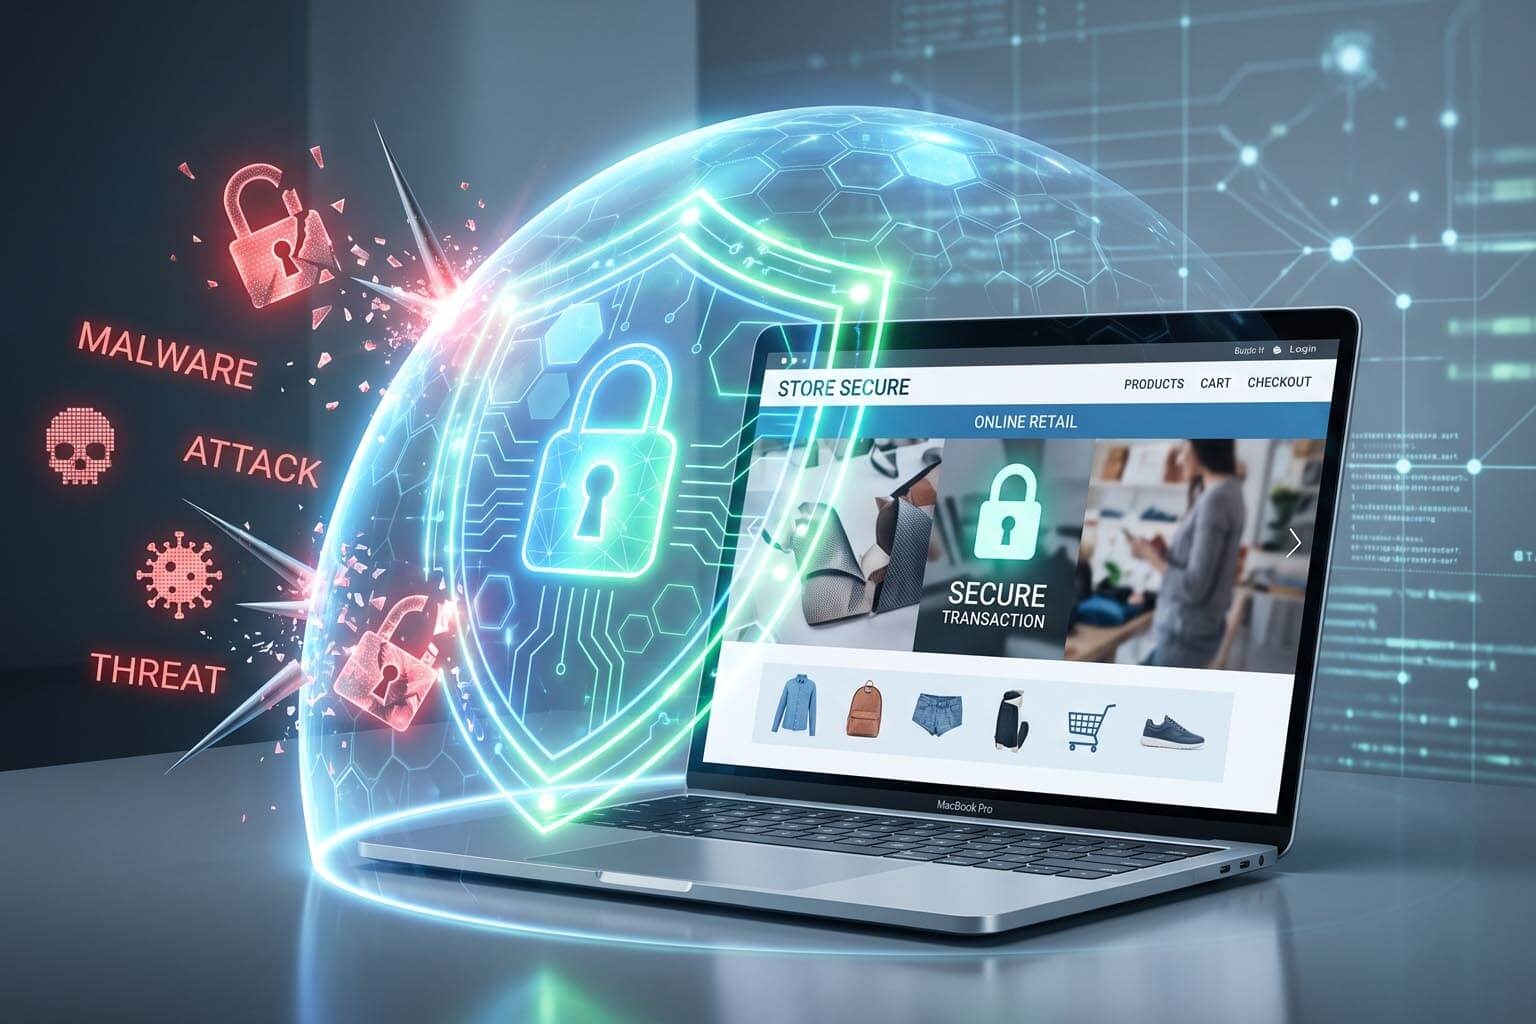
That's the idea behind a security-first website platform.
Instead of treating security as an optional layer added after the website is built, security-first platforms consider protection throughout the architecture, development process, infrastructure, and day-to-day operation of the website.
For online businesses, that difference can matter enormously.
What Is a Security-First Website Platform?
A security-first platform is designed with security as a fundamental requirement rather than an optional feature.
Security is considered across areas such as:
-
Authentication
-
User permissions
-
Data handling
-
APIs
-
Server infrastructure
-
Website requests
-
Forms
-
E-commerce
-
Customer accounts
-
Software updates
-
Monitoring
-
Access control
The objective is not to claim that a platform can never be attacked.
No online system can make that guarantee.
Instead, the objective is to reduce unnecessary attack surfaces, detect suspicious activity, limit potential damage, and make security an integral part of the platform.
Why Website Security Matters More Than Ever
Online businesses increasingly depend on their websites for day-to-day operations.
A website may contain or process:
-
Customer information
-
Contact details
-
Account credentials
-
Orders
-
Business information
-
Product information
-
Transaction information
-
Marketing data
-
Internal content
A security incident can therefore affect much more than the website itself.
It can affect:
-
Revenue
-
Customer trust
-
Business reputation
-
Operations
-
Search visibility
-
Marketing campaigns
-
Internal workflows
For an online business, website security is closely connected to business continuity.
Security Should Start With the Architecture
One of the most important principles in website security is that security shouldn't depend entirely on a single tool.
Imagine a website built using:
CMS + Theme + Plugin + Plugin + Plugin + Security Plugin + External Firewall + Custom Code
Every additional component can potentially introduce another dependency.
That doesn't mean plugins or external services are inherently insecure.
It means every additional component needs to be maintained, updated, configured, and monitored.
A security-first platform can reduce some of this complexity by building important security capabilities into the core platform.
The fewer unnecessary components a business has to manage, the easier it can be to maintain a consistent security posture.
The Problem With Security as an Afterthought
Consider two approaches.
Approach A: Security Later
A business first builds the website.
Then it adds:
-
Security plugins
-
Firewalls
-
Monitoring
-
Login protection
-
Backup tools
-
Spam protection
Security becomes a collection of additional products.
Approach B: Security From the Beginning
The platform is designed with:
-
Secure authentication
-
Access control
-
Input validation
-
Secure APIs
-
Request filtering
-
Rate limiting
-
Monitoring
-
Infrastructure protection
Security becomes part of the underlying system.
The second approach doesn't eliminate the need for additional security measures.
But it can reduce the number of things businesses need to bolt onto their website later.
Every Plugin Is Another Dependency
This is particularly relevant for traditional CMS platforms.
Plugins can be extremely useful.
They provide functionality without requiring custom development.
But every plugin also introduces another piece of software that needs to be maintained.
A business may eventually have plugins responsible for:
-
SEO
-
Security
-
Forms
-
Caching
-
Image optimization
-
E-commerce
-
Analytics
-
Backups
-
Memberships
Each one needs to be compatible with the CMS, theme, hosting environment, and other plugins.
An outdated or vulnerable component can become a security concern.
This is why reducing unnecessary dependencies can be an important part of a security strategy.
Security Updates Matter
Software vulnerabilities are discovered regularly.
Once a vulnerability becomes known, attackers may attempt to exploit websites that haven't been updated.
This creates an ongoing maintenance requirement.
Businesses need to keep track of:
-
CMS updates
-
Plugin updates
-
Theme updates
-
Server software
-
Libraries
-
Dependencies
-
Security patches
The more components a website depends on, the more complicated this process can become.
A platform that centrally manages much of its infrastructure can reduce the maintenance burden for the business.
Authentication Is a Critical Security Layer
A website may have many different users.
For example:
-
Administrators
-
Editors
-
Marketing staff
-
Store managers
-
Support employees
-
Customers
These users should not necessarily have identical permissions.
A modern platform should provide appropriate authentication and authorization mechanisms.
Important capabilities can include:
-
Strong authentication
-
Role-based permissions
-
Secure password handling
-
Session management
-
Account protection
-
Access restrictions
-
Login monitoring
The principle is simple:
Users should have access to what they need—and not more than they need.
Access Control Protects Businesses From Internal Mistakes
Security isn't always about external attackers.
A legitimate user can accidentally:
-
Delete content
-
Change configuration
-
Modify products
-
Expose information
-
Alter important settings
Good access control reduces these risks.
For example, someone responsible for publishing blog posts doesn't necessarily need access to payment settings.
A platform should therefore provide appropriate roles and permissions.
This protects both the business and its employees.
APIs Need Security Too
Modern websites increasingly depend on APIs.
APIs connect websites with:
-
Mobile applications
-
Payment systems
-
CRMs
-
Inventory systems
-
Shipping providers
-
Analytics
-
External business applications
An insecure API can expose sensitive functionality or data.
A security-first platform should therefore treat APIs as a core security concern.
Important areas include:
-
Authentication
-
Authorization
-
Input validation
-
Rate limiting
-
Request monitoring
-
Secure data handling
-
Access control
APIs shouldn't be treated as an afterthought simply because they aren't visible to website visitors.
Input Validation Is Fundamental
Websites constantly receive data from users.
Forms may accept:
-
Names
-
Email addresses
-
Messages
-
Search queries
-
Product information
-
Addresses
-
Account details
That input should never automatically be trusted.
A secure platform should validate and handle input appropriately before processing or storing it.
This helps protect against a range of common web application vulnerabilities.
The principle is simple:
Never assume that user-provided data is safe.
Rate Limiting Can Help Prevent Abuse
Not every malicious request attempts to break into a website.
Some attacks involve overwhelming a particular endpoint with repeated requests.
Rate limiting can help control this type of abuse.
For example, a platform might limit repeated requests to:
-
Login endpoints
-
Forms
-
APIs
-
Search
-
Password reset functionality
This can help protect application resources and reduce certain forms of automated abuse.
Web Application Firewalls Can Add Another Layer
A Web Application Firewall, or WAF, can inspect web traffic and help block certain malicious requests before they reach the application.
A WAF can be useful for protecting against common attack patterns and suspicious traffic.
But a WAF should not be viewed as a replacement for secure application development.
A strong security model is layered:
Secure application + access control + infrastructure security + traffic filtering + monitoring
Each layer addresses different risks.
E-Commerce Needs Even Stronger Security
An online store handles particularly valuable information.
It may process:
-
Customer accounts
-
Orders
-
Addresses
-
Product information
-
Payment-related information
-
Business transactions
A security incident can therefore have serious consequences.
An e-commerce platform should treat security as a core component of:
-
Product management
-
Customer accounts
-
Cart functionality
-
Checkout
-
Order processing
-
Payment integrations
-
Administrative access
Security should be considered at every stage of the customer journey.
Secure Payment Processing Matters
Businesses should avoid treating payment security as simply a checkout-page feature.
The payment architecture should use reputable payment providers and appropriate security practices.
Where possible, businesses should minimize the amount of sensitive payment information that their own systems directly handle.
This can reduce the amount of sensitive information that needs to be stored or processed by the business's infrastructure.
Customer Data Deserves Protection
Customers trust businesses with information.
Depending on the website, that may include:
-
Names
-
Email addresses
-
Phone numbers
-
Addresses
-
Account information
-
Order history
Businesses have a responsibility to handle that information appropriately.
A security-first platform should provide sensible protections around data storage, transmission, access, and administrative controls.
Security isn't only about preventing hackers.
It's also about preventing unnecessary exposure of customer information.
HTTPS Is Only the Beginning
HTTPS is essential for modern websites.
It encrypts communication between the user's browser and the website.
But HTTPS alone doesn't make a website secure.
A website can still have vulnerabilities in:
-
Application code
-
APIs
-
Authentication
-
Plugins
-
Server configuration
-
Access controls
-
Database handling
Think of HTTPS as one important layer rather than the entire security strategy.
Monitoring Matters
Security isn't only about prevention.
Businesses also need to know when something unusual happens.
Monitoring can help identify:
-
Suspicious login attempts
-
Unusual traffic
-
Repeated failed requests
-
Unexpected administrative activity
-
Application errors
-
Infrastructure problems
The earlier suspicious behavior is identified, the faster a business can respond.
This is particularly important for e-commerce businesses that operate continuously.
Backups Are Part of Security
Even with strong security controls, businesses should prepare for failure.
A website could experience:
-
Hardware failure
-
Software problems
-
Accidental deletion
-
Configuration mistakes
-
Data corruption
-
Security incidents
Backups provide a way to recover.
But backups should also be treated as a security asset.
If backups are stored insecurely, an attacker who compromises the main system may potentially affect them as well.
A good backup strategy should consider:
-
Frequency
-
Retention
-
Separation
-
Access control
-
Recovery testing
A backup that cannot be restored reliably isn't much of a backup strategy.
Security and Performance Can Work Together
Security shouldn't automatically mean a slower website.
A well-designed platform can combine security with performance through architecture such as:
-
CDN delivery
-
Efficient caching
-
Request filtering
-
Optimized assets
-
Scalable infrastructure
-
Efficient application processing
The goal is to protect the website while keeping the customer experience fast.
This matters because online businesses need both:
Security and speed.
Security Can Protect SEO and Reputation
A compromised website can have consequences beyond security.
If attackers inject malicious content, redirect visitors, or compromise pages, the website's reputation can suffer.
Search engines may also detect security problems and warn users about unsafe websites.
That can affect:
-
Organic traffic
-
Customer trust
-
Conversion rates
-
Brand reputation
For businesses that rely heavily on search traffic, website security is therefore also part of protecting their digital marketing investment.
Security Builds Customer Trust
Customers may never know which firewall or security system a website uses.
But they notice when a website:
-
Uses HTTPS
-
Provides a secure checkout
-
Protects their account
-
Handles transactions professionally
-
Communicates clearly about privacy
Trust is especially important for smaller businesses.
A customer deciding whether to purchase from an unfamiliar company is already making a judgment about whether the business is legitimate.
A secure, professional website helps reinforce that confidence.
Security Should Be Easy for Business Owners
One of the biggest problems with website security is that business owners often don't have the time or expertise to manage it themselves.
A small business owner shouldn't need to understand:
-
Server hardening
-
Security headers
-
Vulnerability scanning
-
Authentication architecture
-
Rate limiting
-
Firewall rules
-
Dependency management
to operate a reasonably secure website.
The platform should handle as much as possible.
The business should be able to focus on:
Customers → Products → Sales → Growth
rather than:
Plugins → Patches → Security alerts → Compatibility problems
Security-First Doesn't Mean Security-Only
A secure website that is slow, difficult to manage, or impossible to customize isn't a good business platform either.
Security needs to work alongside:
-
Performance
-
SEO
-
Design flexibility
-
E-commerce
-
Scalability
-
Content management
-
Analytics
-
Integrations
The goal is not to build a website that is secure but unusable.
The goal is to build a platform where security is integrated into a good overall business experience.
What Should Businesses Look for in a Secure Website Platform?
Before choosing a platform, businesses should ask:
Is security built into the platform?
Or does it depend heavily on third-party extensions?
How are users protected?
Look for strong authentication and granular access control.
How are APIs secured?
APIs should have appropriate authentication, authorization, and rate limiting.
How are updates handled?
Understand who is responsible for maintaining the underlying software.
What monitoring is available?
Businesses should have visibility into unusual activity and important events.
How are backups handled?
Ask about backup frequency, retention, separation, and recovery.
How does the platform handle e-commerce?
Payment and customer data require additional consideration.
How does the platform respond to vulnerabilities?
A good provider should have a clear process for security issues and updates.
Where RoundRockk Fits
RoundRockk is designed with the idea that security shouldn't be something businesses have to assemble separately from the rest of their website.
Its platform approach brings website building, e-commerce, and security capabilities together rather than requiring businesses to depend on a large collection of separate extensions for basic functionality.
The goal is to reduce unnecessary technical complexity while providing businesses with capabilities such as:
-
Firewall protection
-
IP blocking
-
CAPTCHA protection
-
OAuth2-based authentication
-
Access control
-
Secure APIs
-
Multi-domain capabilities
-
Scalable infrastructure
-
Managed platform security
This approach is particularly relevant for businesses that want more control over their websites without wanting to become responsible for maintaining a large collection of plugins and security extensions.
The philosophy is straightforward:
Security should be part of the foundation, not an attachment added later.
Security Is a Continuous Process
No platform can eliminate every security risk.
New vulnerabilities emerge.
Attack techniques evolve.
Businesses change.
Websites grow.
New integrations are added.
Security therefore needs to be continuous.
Businesses should regularly review:
-
User access
-
Software updates
-
Integrations
-
Backups
-
Monitoring
-
Password policies
-
Administrative accounts
-
Data handling
A security-first platform can reduce the burden, but businesses still need good security practices.
Final Thoughts
For an online business, website security isn't simply a technical feature.
It's part of protecting the business itself.
A compromised website can affect customers, revenue, reputation, search traffic, and day-to-day operations.
That's why businesses should think about security before choosing their website platform—not after something goes wrong.
A modern security-first platform should make security part of the architecture through secure authentication, access control, API protection, monitoring, traffic filtering, backups, and responsible software maintenance.
The objective isn't to create a system that promises to be impossible to attack.
It's to create a system where security is built in, layered, continuously maintained, and easier for businesses to manage.
Because businesses shouldn't have to choose between a website that is easy to manage and one that is secure.
Security should be built into the platform from the beginning.