Website Security Mistakes That Put Ecommerce Stores at Risk
Ecommerce businesses handle sensitive customer information, payment transactions, user accounts, and operational data every day.
As online businesses grow, website security becomes one of the most important aspects of maintaining trust, protecting customer information, and ensuring uninterrupted operations.
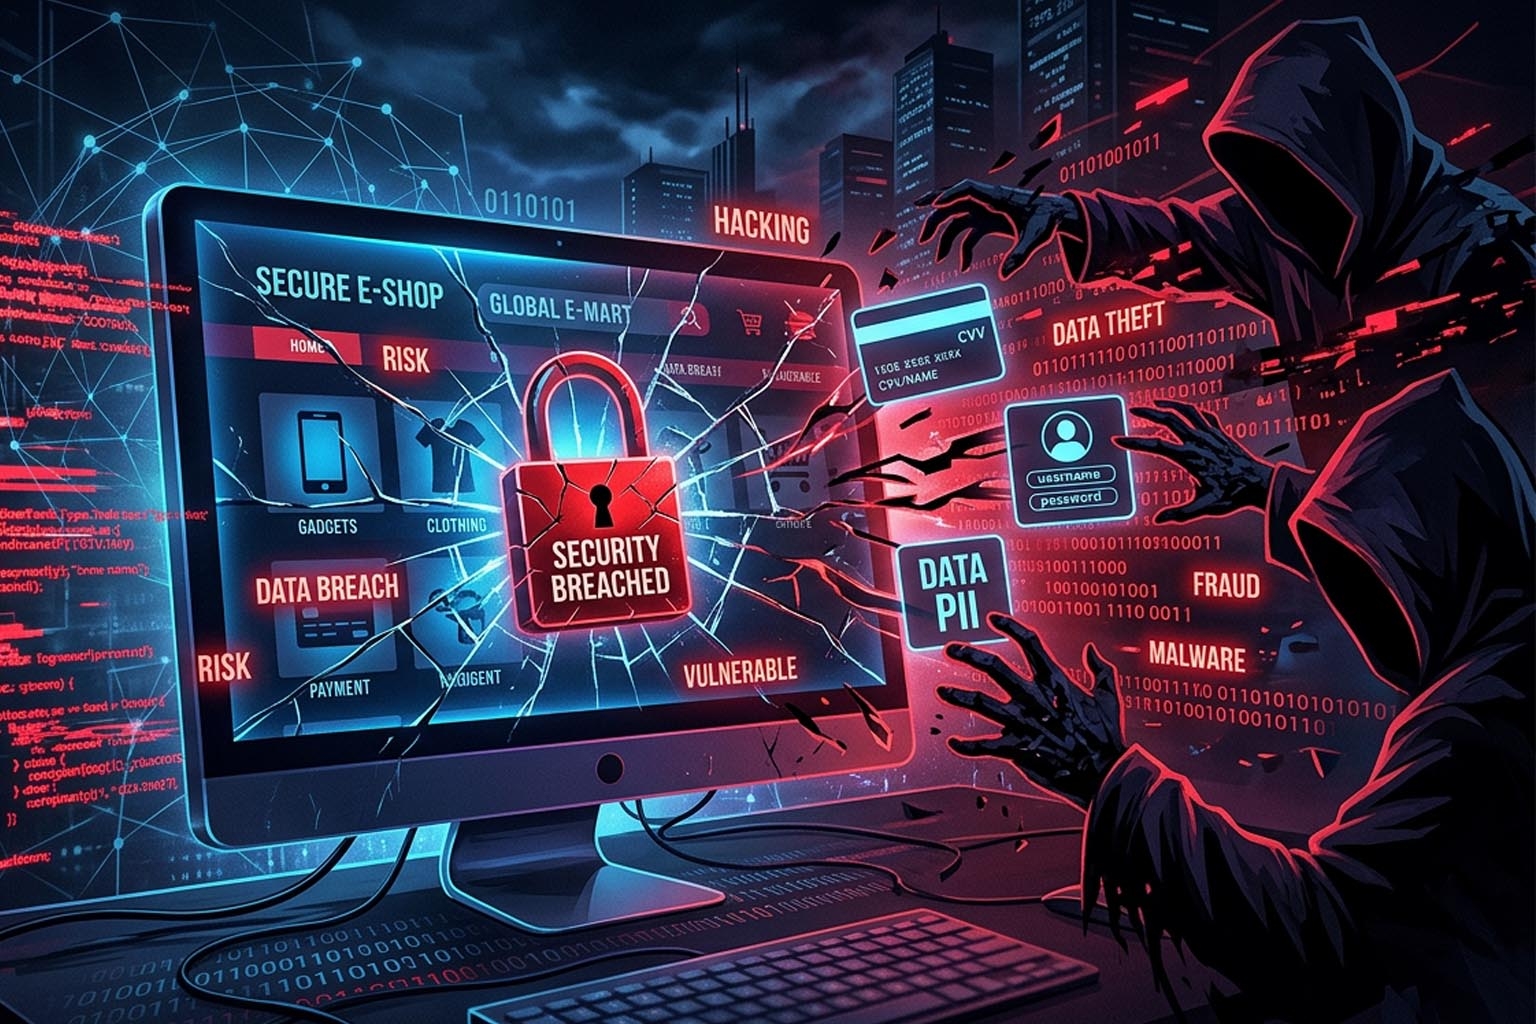
However, many ecommerce stores unknowingly expose themselves to security risks through poor security practices, outdated systems, excessive plugin dependency, weak authentication methods, and fragmented website infrastructure.
Security breaches can lead to:
- customer data exposure
- financial loss
- downtime
- SEO penalties
- reputation damage
- operational disruption
Modern ecommerce security is no longer optional. It is a critical business requirement.
Understanding common website security mistakes can help businesses reduce risks and build safer ecommerce experiences.
Why Ecommerce Stores Are Common Targets
Ecommerce websites are attractive targets because they often contain:
- customer information
- payment data
- user credentials
- order history
- business analytics
- administrative access systems
Attackers frequently target ecommerce stores through:
- brute-force attacks
- malware injections
- plugin vulnerabilities
- phishing attempts
- credential theft
- outdated software exploits
As ecommerce operations scale, security complexity increases significantly.
Common Website Security Mistakes That Put Ecommerce Stores at Risk
1. Using Outdated Software and Plugins
One of the most common security mistakes is failing to update:
- CMS platforms
- plugins
- themes
- extensions
- server software
Outdated systems often contain known vulnerabilities that attackers can exploit easily.
Many ecommerce stores using plugin-heavy systems become vulnerable because:
- plugins stop receiving updates
- compatibility issues delay upgrades
- businesses postpone maintenance
- abandoned extensions remain active
Regular updates are essential for reducing security risks.
2. Excessive Plugin Dependency
Many ecommerce websites rely heavily on third-party plugins and apps for:
- SEO
- forms
- analytics
- customer engagement
- page building
- security
- ecommerce features
Every external plugin introduces another potential security entry point.
Poorly maintained plugins can expose businesses to:
- malware
- unauthorized access
- code injection
- data breaches
The more fragmented the ecosystem becomes, the harder it is to maintain security consistently.
Integrated platforms with built-in functionality reduce this operational risk significantly.
Weak Password and Authentication Practices
Weak authentication remains one of the biggest causes of website compromise.
Common mistakes include:
- weak passwords
- password reuse
- shared admin accounts
- lack of access control
- missing multi-layer authentication
Attackers frequently use automated brute-force tools to target ecommerce login systems.
Businesses should implement:
- strong password policies
- access restrictions
- role-based permissions
- secure authentication systems
to reduce unauthorized access risks.
Lack of Firewall Protection
Many ecommerce businesses underestimate the importance of website firewalls.
Without proper firewall systems, websites become more vulnerable to:
- malicious traffic
- automated attacks
- unauthorized requests
- exploit attempts
Firewalls help filter suspicious activity before it reaches critical website infrastructure.
Security-first ecommerce platforms increasingly include built-in firewall protection to strengthen operational security.
Poor Access Management
As teams grow, businesses often provide admin access to:
- developers
- marketers
- content managers
- customer support staff
- external contractors
Without proper access control, businesses increase the risk of:
- accidental misconfiguration
- unauthorized changes
- internal misuse
- compromised accounts
Businesses should apply:
- role-based permissions
- restricted admin access
- account activity monitoring
- secure authentication workflows
to maintain better operational security.
Missing Backup and Recovery Planning
Many ecommerce businesses only think about backups after a security incident occurs.
Without reliable backup systems, businesses risk:
- data loss
- operational downtime
- broken storefronts
- customer disruption
Security planning should always include:
- automated backups
- recovery procedures
- rollback capabilities
- disaster recovery workflows
This improves resilience during technical or security incidents.
Ignoring Website Performance and Security Relationship
Poor website performance can sometimes indicate deeper infrastructure issues.
Heavy plugins, unoptimized scripts, and fragmented systems can increase exposure to:
- malicious scripts
- server overload
- resource abuse
- security vulnerabilities
Modern ecommerce security increasingly depends on:
- optimized architecture
- centralized management
- controlled integrations
- scalable infrastructure
instead of fragmented ecosystems.
Why Integrated Platforms Improve Security
Modern ecommerce businesses increasingly prefer integrated platforms because they reduce:
- plugin dependency
- external vulnerabilities
- fragmented workflows
- unmanaged integrations
Integrated systems provide more centralized security management.
Instead of depending on multiple third-party tools, businesses can manage:
- ecommerce
- website operations
- authentication
- SEO
- analytics
- customer engagement
inside one controlled environment.
This improves operational stability and security oversight.
How Round Rockk and Rockk Craft Support Ecommerce Security
Round Rockk and Rockk Craft are designed with security-focused architecture to help businesses reduce operational vulnerabilities.
The platform includes:
- firewall protection
- IP blocking
- captcha systems
- OAuth2 authentication
- access controls
- centralized management
inside one integrated environment.
By reducing dependency on fragmented plugins and disconnected systems, businesses can maintain stronger operational security.
Security and No-Code Website Management
Modern businesses want website management systems that are both:
- easy to use
- operationally secure
Rockk Craft combines:
- no-code website management
- WYSIWYG editing
- integrated ecommerce
- visual customization
- centralized controls
while maintaining security-focused infrastructure.
This allows businesses to scale online operations more confidently.
Why Security Matters for SEO and Customer Trust
Website security affects more than operational safety.
Security issues can also damage:
- search engine rankings
- customer trust
- conversion rates
- brand reputation
Search engines increasingly prioritize:
- secure browsing
- HTTPS protection
- stable website infrastructure
- trustworthy user experiences
Businesses with poor security practices may experience long-term SEO and branding damage after security incidents.
The Future of Ecommerce Security
As ecommerce continues evolving, security requirements will become even more important.
Businesses increasingly need:
- centralized systems
- integrated infrastructure
- stronger authentication
- scalable architecture
- reduced external dependency
Modern ecommerce platforms are moving toward security-first ecosystems that simplify operations while reducing exposure to common vulnerabilities.
Conclusion
Website security is one of the most important responsibilities for modern ecommerce businesses.
Common mistakes such as plugin overload, outdated systems, weak authentication, poor access control, and fragmented infrastructure can expose online stores to serious operational risks.
Modern businesses increasingly prefer integrated ecommerce platforms that simplify website management while improving security oversight.
Round Rockk and Rockk Craft are designed to help businesses build secure, scalable ecommerce experiences with integrated security tools, centralized management, and reduced dependency on fragmented systems.
FAQ
Why are ecommerce stores common targets for attacks?
Ecommerce stores often contain valuable customer data, payment information, and administrative systems that attract attackers.
How do plugins create security risks?
Poorly maintained or outdated plugins can introduce vulnerabilities that attackers exploit to gain unauthorized access.
Why is integrated platform security important?
Integrated platforms reduce dependency on multiple external systems, improving operational control and security management.
What security features does Rockk Craft provide?
Rockk Craft includes firewall protection, IP blocking, captcha systems, OAuth2 authentication, and centralized access controls.
How does website security affect SEO?
Security incidents can damage search rankings, customer trust, and overall website credibility.
Looking for a more secure way to manage websites and ecommerce operations?
Explore how Round Rockk and Rockk Craft help businesses build secure, scalable online stores with integrated security tools, visual website management, and centralized operations.